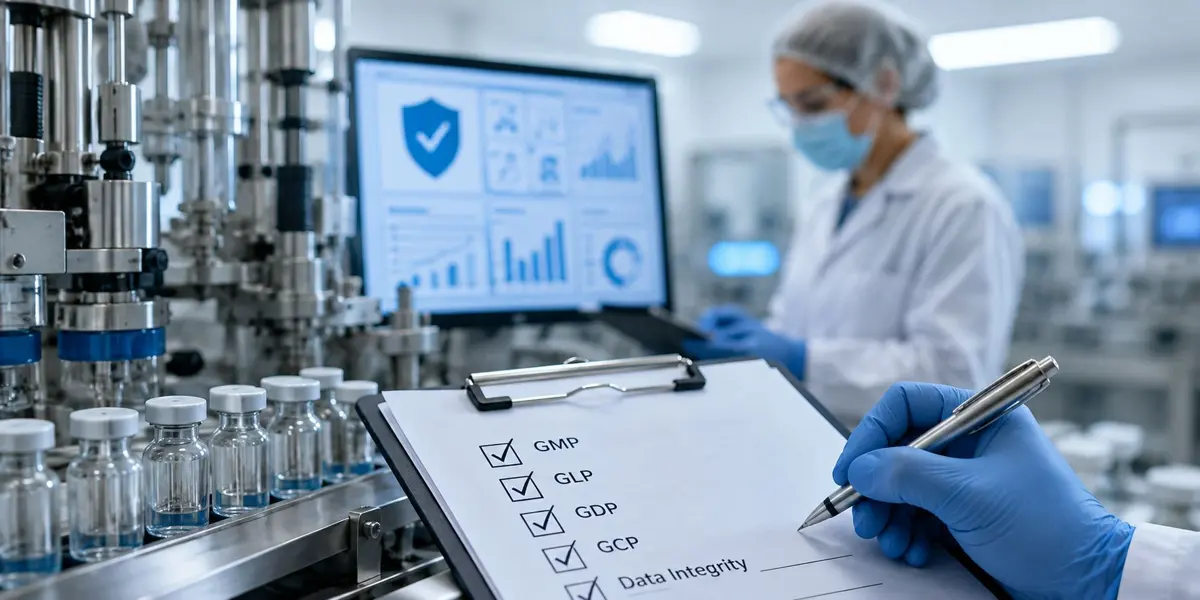
Data integrity is fundamental to pharmaceutical quality because decisions about manufacturing, testing, and product release depend on accurate and reliable records.
During an API supplier audit, auditors examine whether records genuinely reflect the activities performed, whether data can be traced to the individuals who generated or modified it, and whether the quality system protects information from inappropriate changes or loss.
Data integrity applies to both paper-based and electronic records. The ALCOA+ principles provide a useful framework for understanding the expectations for trustworthy data.
1. Understanding ALCOA+
ALCOA+ describes important characteristics of reliable data:
- Attributable: It is clear who performed an activity or recorded the data.
- Legible: Records can be read and understood throughout their retention period.
- Contemporaneous: Information is recorded when the activity takes place.
- Original: The original record or an appropriately verified true copy is available.
- Accurate: Records correctly reflect the activity or result.
The additional principles emphasize that data should be complete, consistent, enduring, and available when required.
During an audit, these principles help auditors evaluate whether manufacturing and laboratory records can be trusted.
2. Shared User Accounts and Weak Access Controls
One potential warning sign is the use of shared login credentials for activities that require individual accountability.
Auditors may review whether:
- Users have unique accounts where required
- Access privileges match individual responsibilities
- Former employees' access is removed appropriately
- Privileged access is controlled
- Changes to user permissions are documented
- System access is periodically reviewed where appropriate
Weak access controls can make it difficult to determine who performed an activity or changed a record.
3. Audit Trails That Are Missing or Not Reviewed
An audit trail records relevant activities or changes within a computerized system, helping preserve the history of electronic records.
Auditors may examine whether relevant audit trails are enabled, protected, retained, and reviewed according to the applicable requirements and risk.
Potential concerns include:
- Audit-trail functionality being disabled without adequate justification
- Changes to critical data that cannot be traced
- Inadequate review of relevant audit-trail entries
- Unexplained changes to laboratory results or processing records
- Audit-trail records that are unavailable when requested
The significance of an issue depends on the system, the data involved, and the applicable requirements.
4. Uncontrolled Data and Incomplete Records
Data-integrity concerns may arise when organizations retain only selected records or cannot demonstrate that the information presented represents the complete set of relevant data.
Examples that may warrant investigation include:
- Missing or unexplained gaps in records
- Uncontrolled spreadsheets used for quality-critical calculations
- Unexplained deletion or repetition of test results
- Inconsistent timestamps or record histories
- Original electronic data that cannot be retrieved
- Differences between raw data, reported results, and approved records
Auditors assess the circumstances and supporting evidence rather than assuming that every discrepancy represents intentional misconduct.
5. Laboratory Systems and Out-of-Specification Results
API laboratory records are particularly important because analytical results support decisions about material quality and compliance with specifications.
Auditors may review:
- Raw data and chromatographic records
- Integration changes and associated justifications
- Original and repeated test results
- Out-of-specification (OOS) and out-of-trend (OOT) investigations
- Review and approval of analytical data
- Instrument access and audit-trail controls
- Data transfer, calculations, and reporting processes
Repeated testing or changes to results should be scientifically justified and handled through approved procedures. Unfavourable results should not be omitted simply because a later result is acceptable.
6. Paper Records and Documentation Practices
Paper-based systems can also present data-integrity risks.
Auditors may examine whether entries are attributable, legible, contemporaneous, and traceable, and whether corrections preserve the original information and include appropriate justification.
Other areas of interest include controlled forms, document revisions, record retention, and reconciliation of issued documents where applicable.
7. What Happens When a Red Flag Is Identified?
A potential red flag should be evaluated using objective evidence and an assessment of its impact on data reliability, product quality, and compliance.
Depending on the findings, appropriate actions may include:
- Documented investigation and root-cause analysis
- Assessment of affected records, batches, or decisions
- Corrective and preventive actions (CAPA)
- Review of system access and data controls
- Assessment of the effectiveness of corrective actions
- Additional supplier oversight or follow-up auditing
The response should be proportionate to the severity and potential impact of the issue.
Conclusion
Effective data-integrity controls help ensure that pharmaceutical manufacturing and laboratory records are reliable, traceable, and suitable for quality decisions.
During API supplier audits, a systematic review of access controls, audit trails, raw data, documentation practices, and investigation records can help identify weaknesses before they undermine confidence in the supplier's quality system.
PharmaTrak's independent GxP audits focus on objective evidence, documented findings, and risk-based assessments to help clients evaluate supplier quality and data-integrity controls.
Regulatory note: This article is for general educational purposes. Data-integrity expectations depend on the applicable regulations, system type, intended use, and relevant quality procedures. Refer to the applicable regulatory guidance, including the FDA's guidance on Data Integrity and Compliance with Drug CGMP, for further information**.